Press Release · Humanix.ai
Humanix Launches Complete Call Context to Expose Voice-Based Social Engineering at the Service Desk
Distributed by Jared Tech · Originally issued via PR Newswire
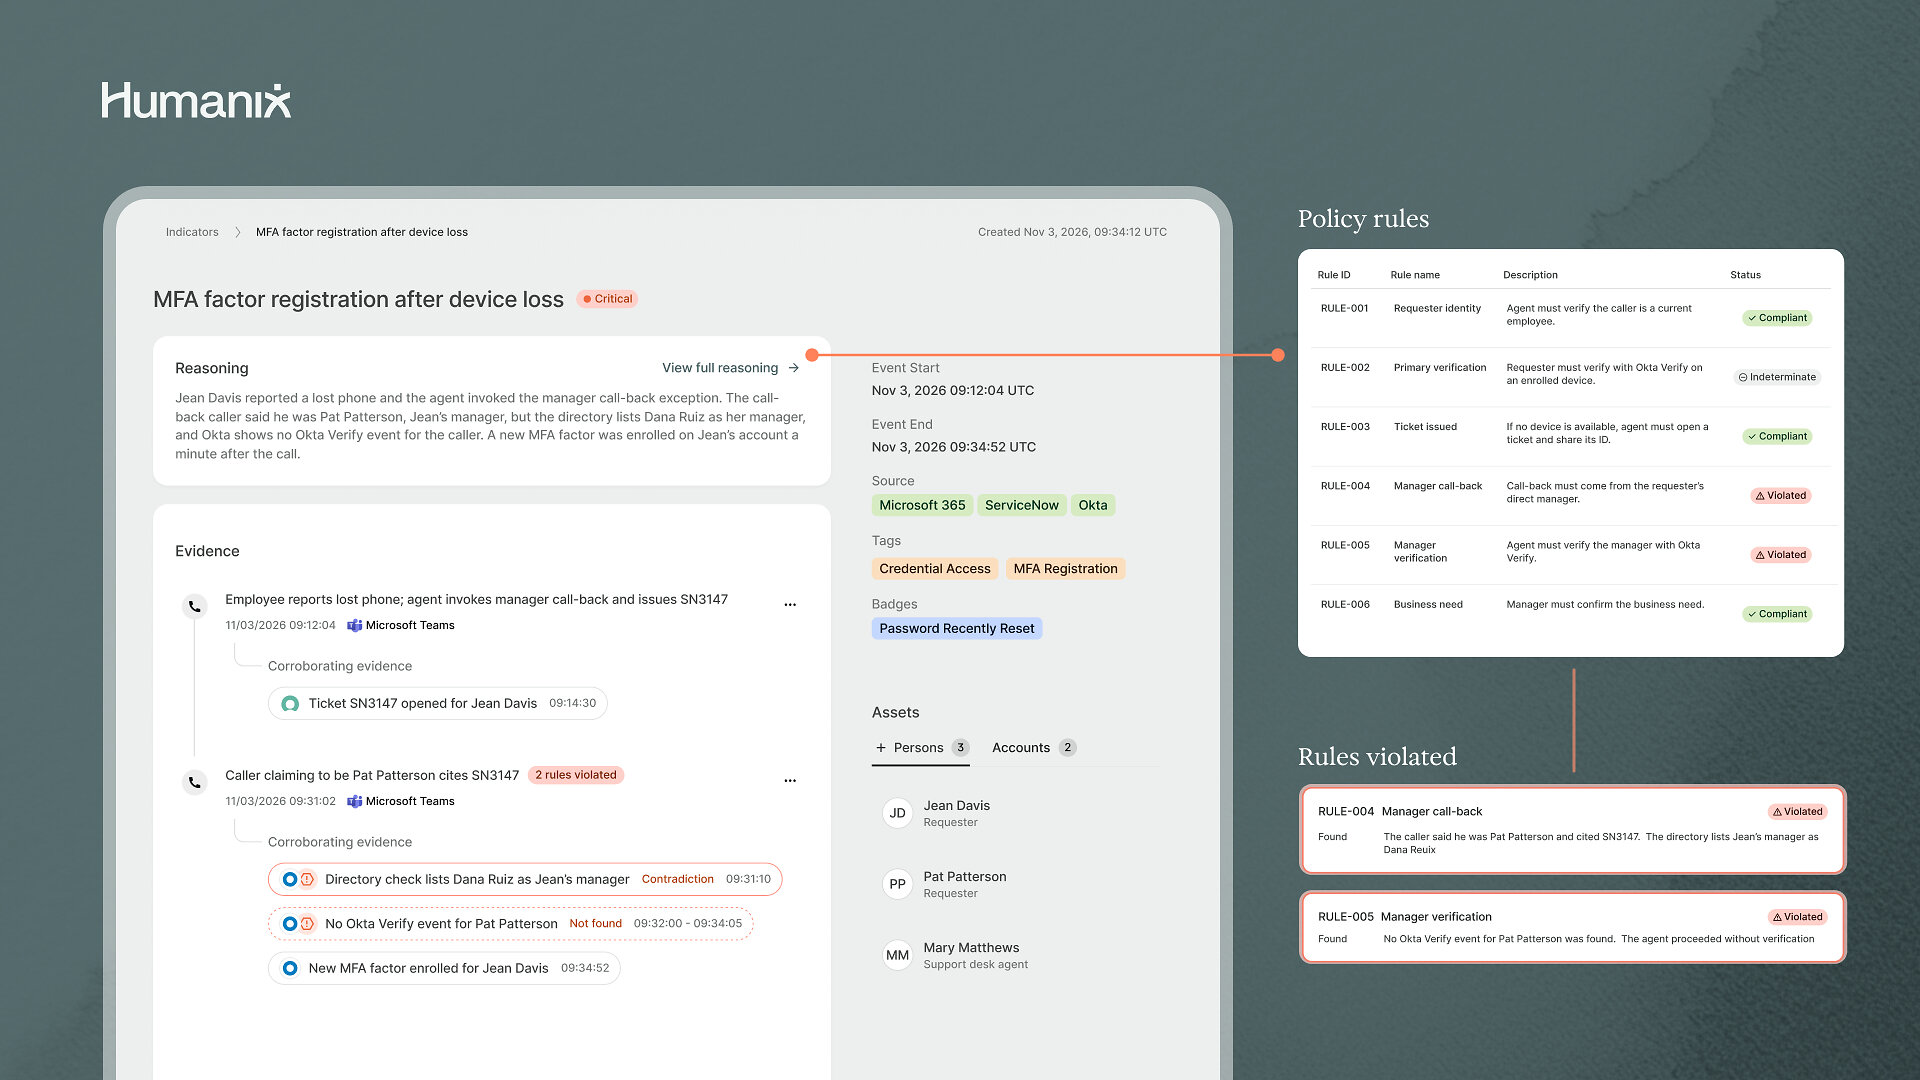
Micro-agents counter the surge in voice attacks by corroborating callers' claims with systems of record
SAN FRANCISCO, Nov. 17, 2026 — Humanix, the company behind the Human Threat Detection and Response platform for social engineering, today launched Complete Call Context to accelerate detection of voice-based attacks against the service desk. Micro-agents now correlate every call with identity records and ticketing data alongside an organization's established procedures. Security teams get the full context behind each password reset, MFA change, or other sensitive request. Any conflict between that evidence and the call triggers an alert.
Complete Call Context arrives as voice phishing, or "vishing," continues to surge. Mandiant reports in M-Trends 2026 that vishing now ranks as the second most common initial infection vector. CrowdStrike found that intrusions using the tactic doubled in the first half of 2026. The SEC has also made the threat an examination priority for 2027.
Many of these vishing attacks target the service desk. An attacker calling the service desk attempts to steal credentials by hijacking a normal password reset or MFA change. These increasingly sophisticated attacks rely on impersonation, urgency, or pressure to skip verification in order to bypass controls. The resulting account change appears routine in identity logs because the call itself leaves few forensic traces. Security analysts rarely see that conversation next to identity provider (IdP) records and IT service management (ITSM) tickets, as these records usually sit in separate systems under IT ownership.
"Correlate suspicious communications and impersonation reports with account recovery events, new devices, privilege changes, and financial transactions to improve threat detection," Gartner® advises CISOs.¹ Humanix correlates each service desk call with the account recovery activity in systems of record. Security teams can then confirm whether a password reset or MFA change matches what the caller claimed.
"AI-assisted attackers can now go from a single phone call to a full compromise in minutes," said Keith Stewart, founder and CEO of Humanix. "Controls that only engage after the call can't keep up. Humanix analyzes the call as it happens, at the first step of the attack. Complete Call Context carries that view into the systems of record to catch those attackers at the point of insertion."
Complete Call Context follows each request from the call to the record
Humanix continuously monitors calls to the service desk for indicators of social engineering, including impersonation of trusted people, manipulation through urgency or authority, and violations of required procedures. Those procedures come directly from each organization. The newly released Complete Call Context creates a micro-agent to analyze each sensitive request, such as an MFA reset. Each micro-agent analyzes the particulars of an individual service request to identify points of context required by the appropriate company procedure. The micro-agent then correlates specific call behaviors with relevant IdP and ITSM records, providing high-fidelity analysis of the complete context of a call. Any contradiction or missing evidence produces an alert with a severity rating and a plain-language explanation.
For example, a caller asks the IT help desk to reset an employee's MFA. The caller claims to manage the employee, requesting to reset MFA on their behalf. However, identity systems list a different person as the employee's manager. The caller cites a ticket number, but the ITSM system has no record of that ticket. The caller indicates the employee had previously verified their identity, but the identity provider shows no record of that verification. Complete Call Context raises an alert that ties these discrepancies to the procedures the call violated.
Security teams act on corroborated evidence
With Humanix, analysts no longer need to reconstruct a voice attack from scattered records. Every alert brings together the call, the account change, and the evidence behind each finding. Containing a compromise while it still affects one account is far easier than recovering from follow-on activity.
Complete Call Context is available now to Humanix customers.
¹ Gartner Press Release, "Gartner Survey Finds 41% of CISOs Reported At Least One Social Engineering Incident Involving a Deepfake in the Past 12 Months," September 22, 2026. https://www.gartner.com/en/newsroom/press-releases/2026-09-22-gartner-survey-finds-41-percent-of-cisos-reported-at-least-one-social-engineering-incident-involving-a-deepfake-in-the-past-12-months
GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.
Media Contact:
Michelle Kearney
Hi-Touch PR
443-857-9468
[email protected]
SOURCE Humanix.ai
About Humanix
Humanix stops social engineering attacks. The Humanix Human Threat Detection and Response platform uses conversational AI to continuously monitor for these attacks on your people across the communication channels where they occur. By detecting social engineering as it happens, Humanix equips you to respond before an attempted attack becomes a breach. The company is backed by Acrew Capital, Boldstart Ventures, and Evolution Equity Partners and was named a 2026 RSAC Innovation Sandbox Top 10 finalist. For more information, visit humanix.ai.